Solutions
Take back control of your custom-built software
Built to measure · fixed quoteIf the program that runs your orders, your warehouse or your invoicing was built by someone who is no longer around, or by a supplier who no longer answers, we audit it in one week: what you have, what state it is in, what risks you run and what it costs to maintain or replace it. Then we maintain it, adapt it or replace it. You decide.
The application
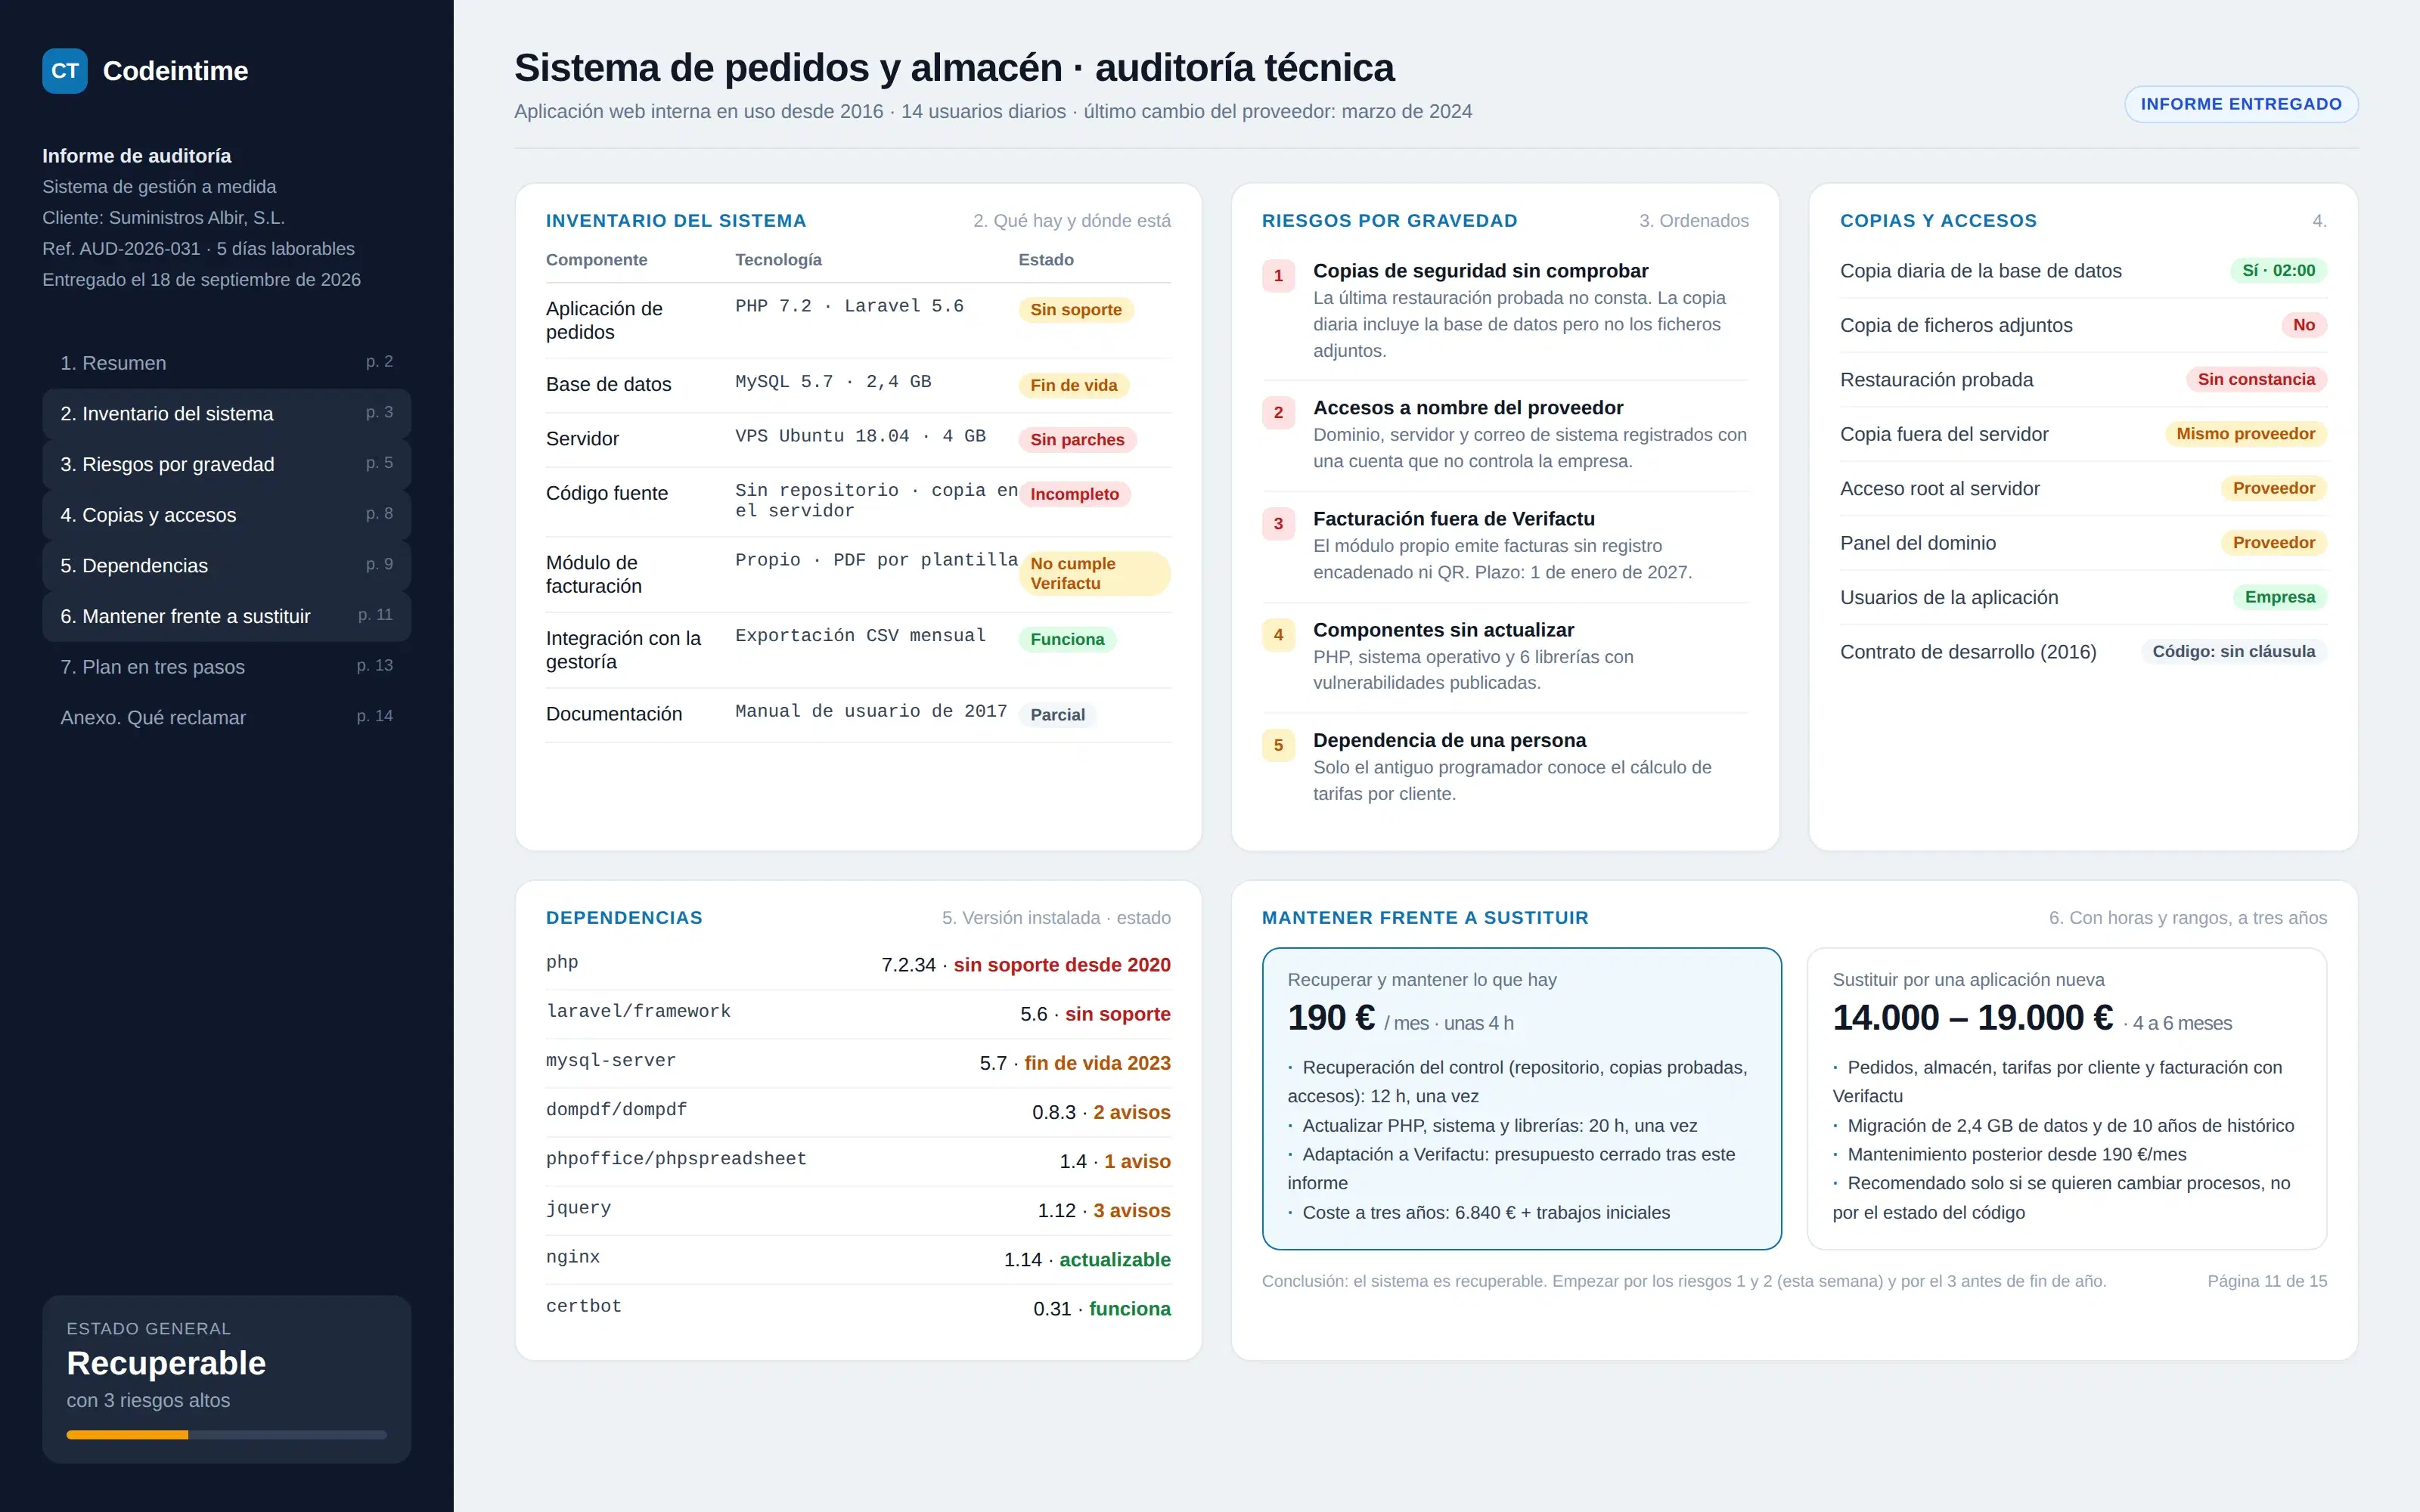
This is the audit report
A written document, not a slide deck: system inventory, state of the code and the backups, risks ranked by severity, dependencies with their versions and the cost of maintaining it against the cost of replacing it, with hours and ranges. It ends with a three-step plan to start with what is urgent.
Example with fictitious data. The report on your system is delivered as a PDF and is yours.
Features
Everything it does for you from day one, without anyone having to remember.
Inventory of what you have: which applications exist, where they are hosted, what they are built with, which versions and which dependencies they use.
Real state of the code: whether it exists, whether it is complete, whether it is documented, whether there is a change history and whether it can be continued.
Risks ranked by severity: access and passwords, backups (and whether they actually restore), outdated components, dependence on a single person, legal compliance.
Cost of maintaining it as it is, with estimated hours per month, and cost of replacing it if that paid off, with a range and timescales.
Taking back control: code repository, tested backups, access in your company's name and documentation so that anyone can continue it.
Corrective and evolutionary maintenance afterwards, and whatever the law or the business requires: Verifactu before 1 January 2027, automations, connections to other systems.
How it works
- 1
You give us read access to the code and the server, or tell us who has it, and half an hour with someone who uses the system every day. If a contract with the supplier exists, we look at it too.
- 2
In five working days we review code, database, server, backups and access. If there is no access to the code, we audit what is reachable and the report says what to claim and on what grounds.
- 3
We hand you the written report: inventory, state of the code, risks by severity, cost of maintaining versus replacing and a three-step plan. The report is yours and is useful even if you stay with whoever runs it today.
- 4
If you want us to carry on, we start with what is urgent: taking back control (repository, backups, access). Then monthly maintenance, Verifactu adaptation, automations or replacement, at a fixed price.
The law, in detail
The GDPR requires being able to restore data and testing it; Verifactu requires the software that invoices to meet the regulation from 2027. Both obligations fall on the company, not on the supplier who is no longer there.
The law, in detail
The GDPR requires being able to restore data and testing it; Verifactu requires the software that invoices to meet the regulation from 2027. Both obligations fall on the company, not on the supplier who is no longer there.
Article 32 of the General Data Protection Regulation requires the controller to apply technical and organisational measures appropriate to the risk, and lists among them the ability to restore the availability of and access to personal data in a timely manner in the event of a physical or technical incident, and a process for regularly testing, assessing and evaluating the effectiveness of those measures. A custom-built program where nobody knows whether the backups restore, who holds the passwords or where the code is does not meet that article, and the liability lies with the company using it. If the system issues invoices or receipts, Verifactu is added: Ley 11/2021 (art. 29.2.j of the Spanish General Tax Law) and Real Decreto 1007/2023 require every computerised invoicing system, including custom-built ones, to generate chained, tamper-proof records, include a QR code on each invoice and be able to send the records to the Spanish tax authority, from 1 January 2027 for companies and 1 July 2027 for everyone else. Adapting a program without a supplier first requires knowing what is inside. That is the audit.
- Norma
- Regulation (EU) 2016/679 (GDPR), art. 32 · Ley 11/2021, art. 29.2.j) LGT · Real Decreto 1007/2023
- If you do not
- Invoicing with a system that does not meet Verifactu carries a fine of €50,000 per financial year (art. 201 bis LGT). And if you cannot restore your data after an incident, the liability under the GDPR is your company's, not that of whoever wrote the program.
Who it is for
The person who built it is gone
An employee or a freelancer built the program years ago and no longer works with you. Nobody else has touched the code.
Suppliers absorbed or closed down
The company that built it closed, its owner retired or a large group bought it and now everything goes through a ticket portal.
Changes that take weeks
The supplier is still there, but every change takes weeks and costs whatever they say, and nobody can explain why.
Systems that invoice and must meet Verifactu
In-house invoicing software or POS terminals that must be adapted before 1 January 2027, with no one clearly in charge of doing it.
What it costs
Audit €490 · fixed price · report in one week
The audit costs €490, a fixed price with no extras, and the report is delivered within five working days of receiving access. The report is yours: it is just as useful if you decide to stay with whoever runs it today. If you then hire us for the work: maintenance from €190/month with no lock-in; automation of one process, €1,900 plus €90/month; replacement or Verifactu adaptation, at a fixed price based on the report.
Tell us about your case
Two lines are plenty. We reply within 24 working hours.